
The organizational chart with the right job titles will not get you licensed. What the regulator is looking for is a compliance architecture: documented independence, collective expertise across three distinct knowledge domains, and real institutional substance. This is how that standard works in practice.
MiCA Decoded is a 12-article weekly series for Bitcoin.com News, co-authored by LegalBison’s Co-Founding and Managing Directors: Aaron Glauberman, Viktor Juskin and Sabir Alijev. LegalBison advises crypto and FinTech companies on MiCA licensing, CASP and VASP applications, and regulatory structuring across Europe and beyond.
The Myth: Outsourcing a Compliance Officer Is Enough
When founders begin planning for crypto-assets services providers (CASP) authorization, the conversation almost always arrives at the same moment: “So, do we need to hire a compliance officer?”
Sometimes the question comes with a follow-up: “And a Money Laundering Reporting Officer (MLRO)? Is that it?”
The answer to both is yes. But treating those two appointments as the finish line is the most common and consequential misreading of what MiCA actually demands from a compliance function.
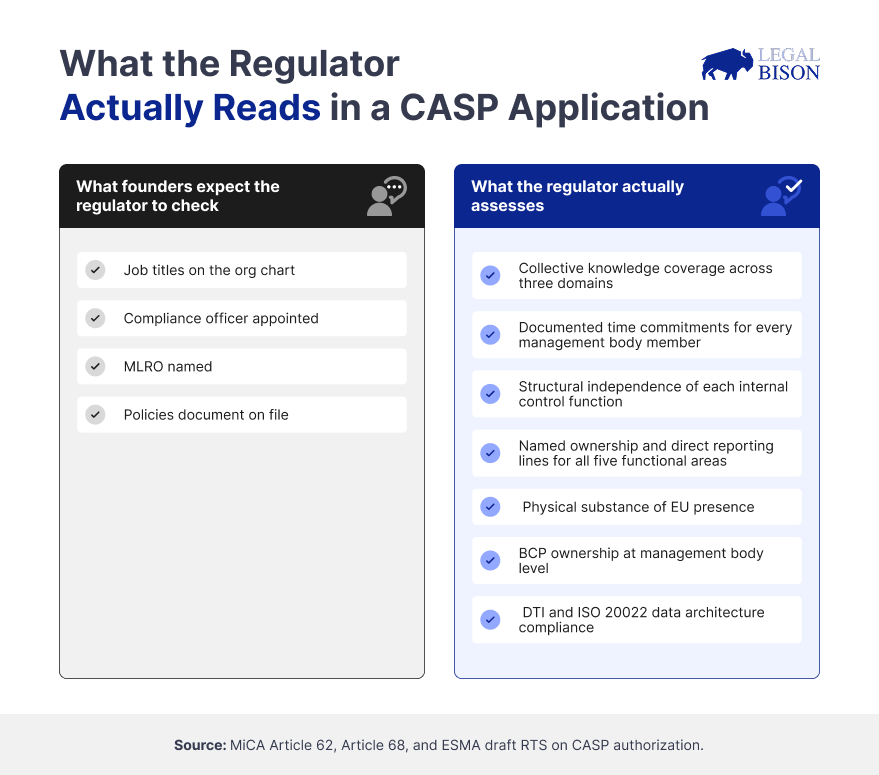
Regulators are not checking whether the org chart has the right job titles. They are assessing whether the management body, as a whole unit, has the knowledge architecture, the structural independence, and the documented operational depth to run a regulated financial institution. A MiCA license is not issued to a person. It is issued to an organism.
This distinction sits at the heart of why so many early-stage applications stall or require significant rework before a National Competent Authority (NCA) will grant authorization.
What “Collectively” Actually Means in the Regulation
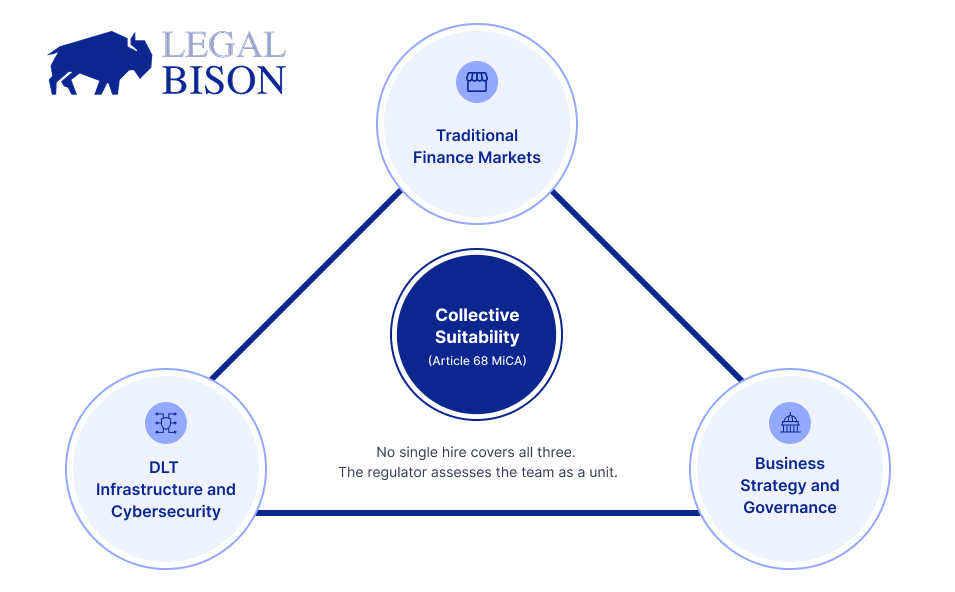
Article 68(1) of MiCA is precise on this point. Members of the management body must possess the appropriate knowledge, skills, and experience “both individually and collectively”. That single word, “collectively,” is doing significant regulatory work.
The joint EBA and ESMA guidelines on suitability of management body members and shareholders for entities under MiCA make the mechanics of that standard explicit by listing the specific areas of professional experience the management body must possess. Eira Järvi, Senior Lawyer at LegalBison, has outlined the specific requirements in the table below.
When you analyze ESMA’s guidelines, it becomes clear that the management body’s combined profile must demonstrably cover three core knowledge domains, which include all those detailed by Eira:
- Traditional financial markets: Regulatory frameworks, investor protection obligations, market conduct rules, and the operational standards that apply to licensed financial service providers.
- Digital Ledger Technology (DLT) infrastructure and cybersecurity: Blockchain architecture, protocol-level risk, smart contract exposure, cybersecurity threat modelling, and the specific operational vulnerabilities that arise from on-chain service delivery.
- Business strategy and organizational governance: Risk management design, internal control architecture, governance policy, and the ability to assess and periodically review the firm’s compliance effectiveness.
The regulator is not expecting one person to hold all three domains. The expectation, formalized by ESMA’s requirement that firms submit an assessment of their “collective suitability”, is that the team, taken together, covers all of them without meaningful gaps.
A management body drawn entirely from traditional finance backgrounds, with no one capable of evaluating DLT infrastructure risk, is structurally incomplete before the application is submitted.
The same applies in reverse: a technically deep crypto-native team with no one who understands regulated financial markets conduct will face the same scrutiny.
The Time Commitment Problem Nobody Talks About
There is a second layer to the collective suitability standard that catches applicants off guard.
The right people must exist in practice, not just on paper. Each member of the management body must document, in writing, their minimum time commitment to the firm: specifically, an estimation of the time devoted to the role (with both annual and monthly indications), alongside a formal declaration of all other executive and non-executive directorships currently held.
ESMA’s draft regulatory technical standards on authorization (drawn from the first consultation package) are explicit on this. The assessment covers whether each person is functionally present, not just nominally listed.
A non-executive with four other board seats and a compliance advisory relationship with two additional firms will face direct scrutiny. The NCA needs to be satisfied that the management body can actually perform its duties, not just that the right names appear on the application.
This matters most for early-stage crypto firms that bring in experienced compliance figures in a part-time or advisory capacity to strengthen an authorization application. The regulator will see exactly how many hours per month that person is committing, and it will compare that figure against the scope of the role and the services the firm intends to provide.
A mismatch between responsibility and time commitment is a red flag, not a technicality.
The Internal Control Functions: Structure Over Titles
Understanding collective suitability at the management body level is only part of the picture. MiCA Article 68(4) requires CASPs to adopt policies and procedures “sufficiently effective to ensure compliance.” Article 68(5) requires personnel with appropriate knowledge at every level of the firm. Article 68(6) requires the management body to periodically review the effectiveness of those arrangements and address any deficiencies found.
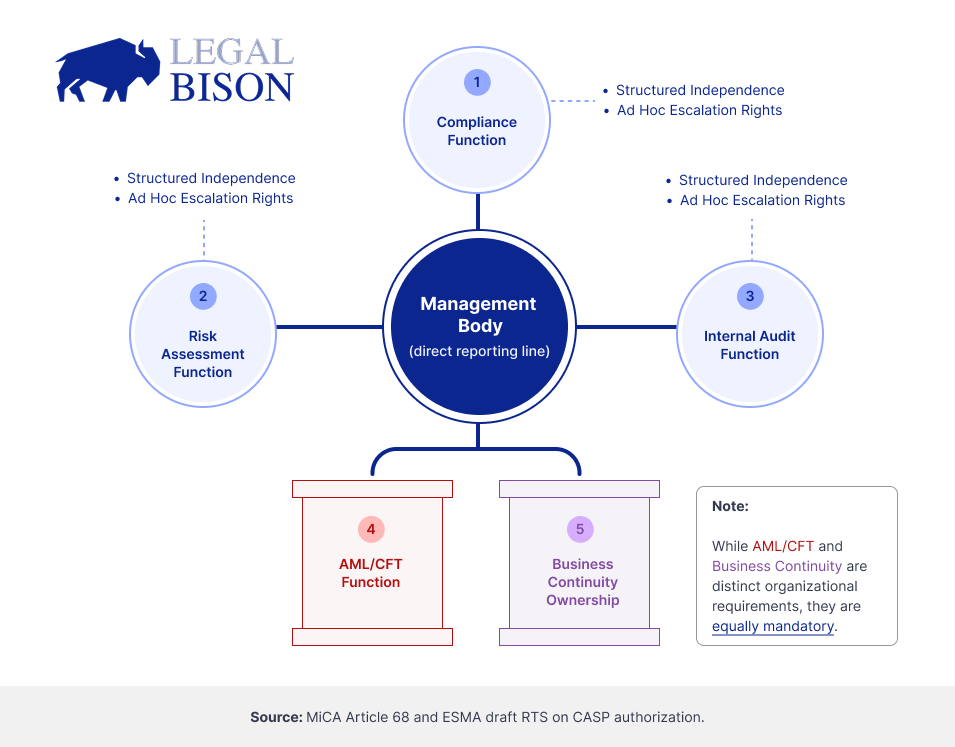
ESMA’s draft RTS take this further. They require firms to identify specific internal control functions and document, for each one:
- The reporting line runs directly to the management body.
- How the function operates independently from the business area it oversees.
- How the function can access the management body on a scheduled basis and on an emergency (ad hoc) basis when a significant compliance risk is detected.
The three functional areas that form the core of this internal control framework are:
- The compliance function (regulatory obligations, conduct policies, internal procedures).
- The risk assessment function (risk identification, assessment methodology, escalation protocols).
- The internal audit function (independent effectiveness review, periodic assessment).
Note: The AML/CFT function and the Business Continuity function are also mandatory pillars of the authorization application, but ESMA treats them as distinct organizational requirements alongside this core internal control framework.
MiCA does not always assign these precise labels at the Level 1 text. The ESMA RTS make clear that these core internal control areas must have named owners, documented scopes of responsibility, and verified structural independence.
That last point is where many applications reveal a structural flaw.
A compliance function that reports to the Chief Operating Officer, who also manages revenue and business development, is not independent in the regulatory sense. A risk function embedded within the trading desk, reporting upward through the same chain as the desk it is supposed to monitor, does not meet the standard either.
The regulator will request the organizational chart. It will then ask who the compliance head reports to in practice, what that person’s other responsibilities are, and what escalation rights they hold when a serious compliance risk is identified.
Building a CASP license application around a real independence structure requires that the architecture be designed before the application is drafted, not retrofitted afterward.
Physical Substance: The Nominee Director Problem
The authorization application must document a physical place of effective management inside the EU. This means the head office address, branch locations where relevant, and the genuine decision-making geography of the firm.
- At least one director exercising real authority must be resident within the Union and accessible to the NCA of the home member state.
- A registered address in an EU jurisdiction supported by a nominee director arrangement does not satisfy this standard.
- The substance requirement means that human decision-making weight must actually sit inside the Union.
NCAs assess this through the location fields in the RTS application and through the time-commitment disclosures of each management body member.
A director who is physically present in the EU for two weeks per quarter does not qualify as a resident director in any meaningful regulatory sense.
This is a point that matters particularly for firms operating from global headquarters outside the EU that are building toward a crypto license in Europe. The EU-based entity must function as a real decision-making unit, not as an administrative front for a group structure operating from elsewhere.
Business Continuity Belongs to the Compliance Team
Business continuity is widely treated as an IT responsibility. Under MiCA and the Digital Operational Resilience Act (DORA), that framing is incorrect for any authorized CASP.
The Business Continuity Policy must be owned, approved, and maintained by the management body. DORA (Regulation EU 2022/2554) governs the elements specific to information and communications technology, and CASPs fall within DORA’s scope as financial entities. The two frameworks operate simultaneously, and the compliance function must be capable of navigating both at once.
ESMA’s second MiCA consultation paper introduced a specific obligation for firms operating on permissionless distributed ledger technology (public blockchains such as Ethereum): proactive, structured communication with clients during any DLT-level service disruption.
The firm must update clients on whether their funds are at risk and provide a clear picture of how service resumption is being managed. The firm remains fully liable for any losses arising from its own smart contracts, regardless of whether the underlying blockchain is permissionless.
This is not a standard IT outage policy. Owning this obligation meaningfully requires the management body to understand DLT infrastructure risk at a level that goes well beyond general technical awareness.
The compliance team that can only describe blockchain risk in general terms will not be able to draft, review, or maintain a business continuity policy that satisfies regulatory scrutiny.
Data Standards as a Compliance Capability
The compliance function’s responsibilities extend into data architecture. CASPs operating trading platforms must use the Digital Token Identifier (DTI) standard for all record-keeping and reporting to NCAs. The DTI uniquely identifies each crypto-asset and links it to the specific DLT on which it is issued, traded, or settled. This allows regulators to perform cross-border surveillance with consistent, comparable data.
ISO 20022 messaging standards govern the format of transactional data submitted to authorities. Pre- and post-trade transparency data must be disclosed through non-discriminatory, machine-readable public channels to prevent market abuse. Each of these requirements has a technical dimension that the compliance team must own, not delegate blindly to IT.
A firm that treats record-keeping as a general system administration task, without compliance oversight of the specific data standards the RTS demands, will face supervisory problems after authorization.
The standards exist precisely so that NCAs can compare records across hundreds of CASPs in a single analysis. A firm that cannot produce data in the required format is a firm that cannot demonstrate ongoing compliance.
This is the practical meaning of the “single brain” standard. The compliance team integrates regulatory awareness, governance structure, DLT operational knowledge, and technical data literacy as a single functioning capability. None of those elements can be outsourced entirely to another function.
Building the Team Before Building the Application
The authorization application for a CASP MiCA license documents an institution that already exists. That is the mental model that separates firms that move efficiently through the process from those that stall.
Firms pursuing crypto exchange licensing, digital asset custody authorization, or any other CASP license in Europe need to approach team architecture as the first deliverable, not as something that comes together while the application is being drafted.
The compliance function must be structurally independent before the first document is written. The management body’s collective knowledge coverage must be assessed and any gaps addressed before the NCA review begins. The time commitment disclosures must be realistic before they are submitted.
The same logic applies globally. Firms applying for a VASP license in jurisdictions outside the EU are increasingly encountering parallel standards: regulators in the Middle East, Asia-Pacific, and the Americas are converging on similar substance-over-form requirements for compliance function design.
The EU standard, which is the most detailed and technically specific currently in force, is a useful benchmark for any team building toward regulated status in any major jurisdiction.
Key Takeaway
The myth: Appointing a compliance officer and an MLRO satisfies MiCA’s compliance obligations.
The reality: MiCA requires a functioning compliance organism, not a list of job titles.
Three things determine whether a management body meets the standard:
Collective knowledge coverage. The team, taken as a unit, must cover traditional financial markets expertise, DLT and cybersecurity proficiency, and organizational governance capability. Gaps in any one domain are structural deficiencies, not profile preferences.
Documented structural independence. The core internal control functions (compliance, risk assessment, and internal audit) must have a named owner, a direct reporting line to the management body, and verified independence from the business area they oversee. (Note: AML/CFT and business continuity are equally mandatory, but treated as distinct organizational pillars). An org chart that routes compliance through a revenue-generating function will not survive NCA scrutiny.
Real institutional substance. Time commitments must be genuine and documented. The EU physical presence must reflect actual decision-making weight, not a registered address. The business continuity policy must be owned at the management body level. Data reporting must meet DTI and ISO 20022 standards from day one.
The CASP license application is the output. The compliance architecture is the foundation. Build the foundation first.

This article is based on a study conducted by LegalBison in April 2026. The content is for informational purposes only and does not constitute legal advice.