
The most misleading phrase in crypto security may also be the most familiar one.
A smart contract can execute exactly as written and still become part of a theft. If you wonder how, have you considered that the code may never be the part that breaks?
We blame smart contracts (the code), but the real vulnerability is the humans running the project. Attackers aren’t finding brilliant math flaws; they are tricking a founder into clicking a bad link, stealing their computer’s access keys, and altering the app from the inside. Yet once funds move on-chain, these failures often get flattened into the same headline category. Yep, you guessed it right – A DeFi hack!
That is the diagnosis problem.
A smart-contract bug, a bridge-signature compromise, an oracle failure, a governance abuse path and a stolen private key do not describe the same wound. Once the failure is misnamed, the fix starts in the wrong place.
Ethereal Ventures recently framed this as a control-plane problem – The security of the systems around the protocol, not only the protocol logic itself. AMBCrypto takes that argument in a narrower direction. In fact, before the industry debates the fix, it needs to name the failure correctly.
Of course, the data makes the mislabeling harder to ignore. For example, Halborn found that in 2024, off-chain incidents made up 56.5% of attacks and 80.5% of stolen funds.
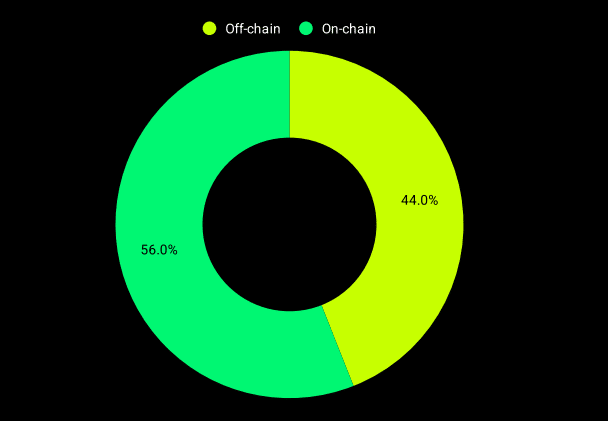
Chainalysis also found that private-key compromises accounted for the largest share of stolen cryptos in 2024.
So, the uncomfortable question is simple: Is “better code” enough when the attacker’s best path is stealing the key that tells the code what to do?
If most losses are coming from off-chain weaknesses, why does the industry keep calling every major incident a DeFi hack?
A headline is not a diagnosis
“DeFi hack” works as a headline because it is short. It fails as a diagnosis because it hides the thing that actually broke.
Ritesh Kakkad, Co-founder of XDC Network, put it bluntly when he said,
The term DeFi hack has done a lot of damage. Not because it’s wrong, but because every time something breaks we use it as a full stop instead of a starting point. Ronin, Nomad, both got filed under the same label but they were trust architecture failures, nothing to do with contract quality.
That distinction matters.
So, what actually broke?
A stolen private key, a bridge-validator failure, a poisoned interface and broken protocol logic may all end with funds moving on-chain. But they begin in different places.
This brings us to where the knowledge of the application plane and control plane helps.
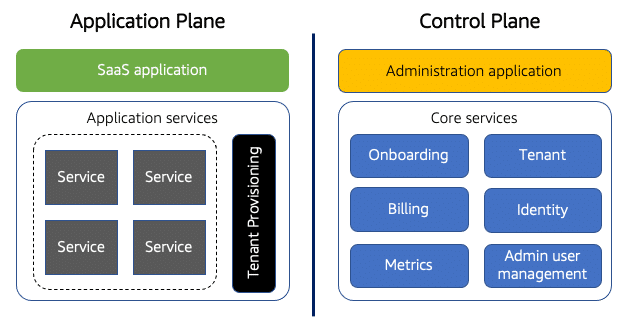
The application plane is what users touch and includes swaps, lending markets, vaults, transfers and bridge activity. The control plane is what gives the system authority to act: admin keys, signers, upgrade paths, bridge validators, oracles and governance permissions. Then, there is the human and operational layer around it: devices, GitHub access, CI/CD pipelines, cloud accounts, contractor permissions and incident response.
And yet, most public narratives collapse these layers into one word – Hack.
Imagine opening a DeFi app and approving what appears to be a routine transaction. The page looks familiar. The wallet prompt seems normal. The blockchain later records a valid approval. But what if the screen was altered before the signer ever saw it? What if the failure sat in the app interface, the access credentials, or the workflow around the signing process?
How does crypto security compare to traditional tech companies?
Traditional enterprise systems usually separate these failures because each one triggers a different response. Crypto often loses that precision once the stolen funds land on a block explorer.
| Operational layer | Enterprise tech norm | Common Web3 weakness |
|---|---|---|
| Access control | Limits who can log in, from which device, and with what approval. | Admin duties are conducted on personal laptops, with core team members often coordinating multi-million dollar actions over standard Telegram or Discord chats. |
| Control plane | Layered approval systems and audit trails | Multisig can still leave too much power with a small group of people and keys. |
| CI/CD | Separates testing, approval, and release, so bad updates are harder to push live. | Compromised credentials can alter what users or signers see |
Failure mode changes from case to case
The post-mortems (or evidence) tell a more complicated story than the headlines. Most crypto post-mortems begin too late. They ask, “How much was stolen?” before asking, “What actually failed?”
Look at Ronin, for instance, remembered as one of crypto’s defining bridge hacks. In March 2022, attackers drained 173,600 ETH and 25.5 million USDC from the Ronin Bridge. However, the mechanics matter here.
Ronin’s bridge needed 5-of-9 validator signatures to approve withdrawals. The attacker did not need to find a conventional smart-contract bug to get there. Four Sky Mavis validator keys were compromised. The fifth approval came through an old Axie DAO permission path linked to Ronin’s gas-free RPC setup, which had not been properly revoked.
Once those five approvals were in place, the bridge treated the withdrawals as valid.
That is the part the “bridge hack” label tends to flatten. The weak point was not simply the bridge as a product, or DeFi as a category. It was the authority structure around the bridge: who could approve movement, how those approvals were protected, and why an old access path was still capable of mattering.
It’s the same story elsewhere
Ronin was not an exception. Orbit Chain, WazirX and Bybit all point to the same pattern from different angles. Even the wrench attack incidents in France belong in the broader diagnostic conversation. They were not DeFi failures, but they showed the same uncomfortable truth: attackers follow control, whether that control sits in code, a multisig, a browser interface, or a person.
Where is the money going?
The broader data complicates the usual story too.
Immunefi recorded $1.635 billion in crypto losses across 40 incidents in Q1 2025. They tagged it the worst quarter for hacks in crypto’s history. But the split matters.
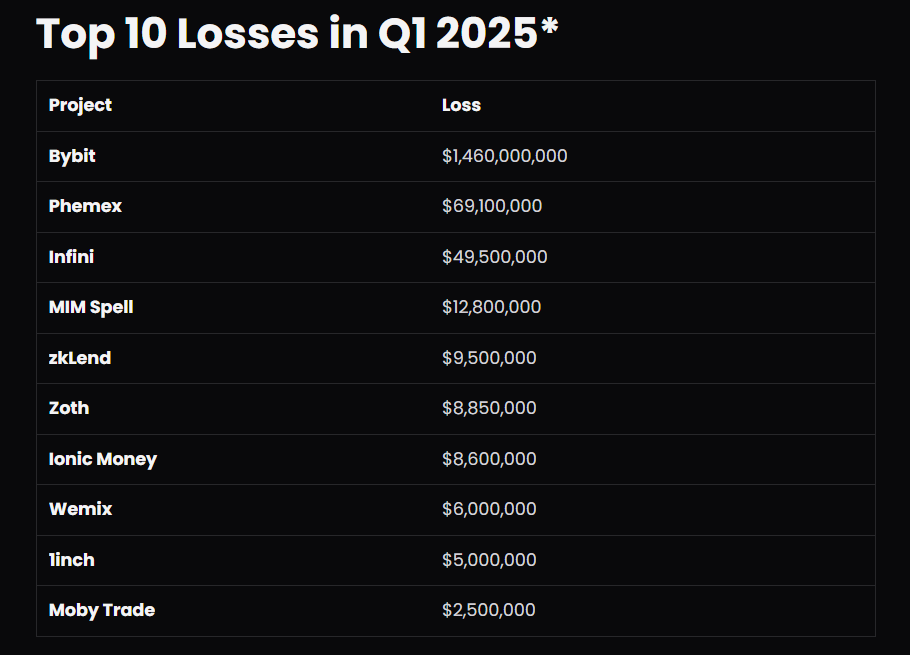
Most of that figure came from two CEXs. And together, those incidents accounted for roughly 94% of the quarter’s losses.
That does not mean DeFi risk disappeared. But by value, the quarter was dominated by CeFi and signing-related failures, not a wave of protocol-math breaks.
Chainalysis’ report on theft highlighted something similar too.
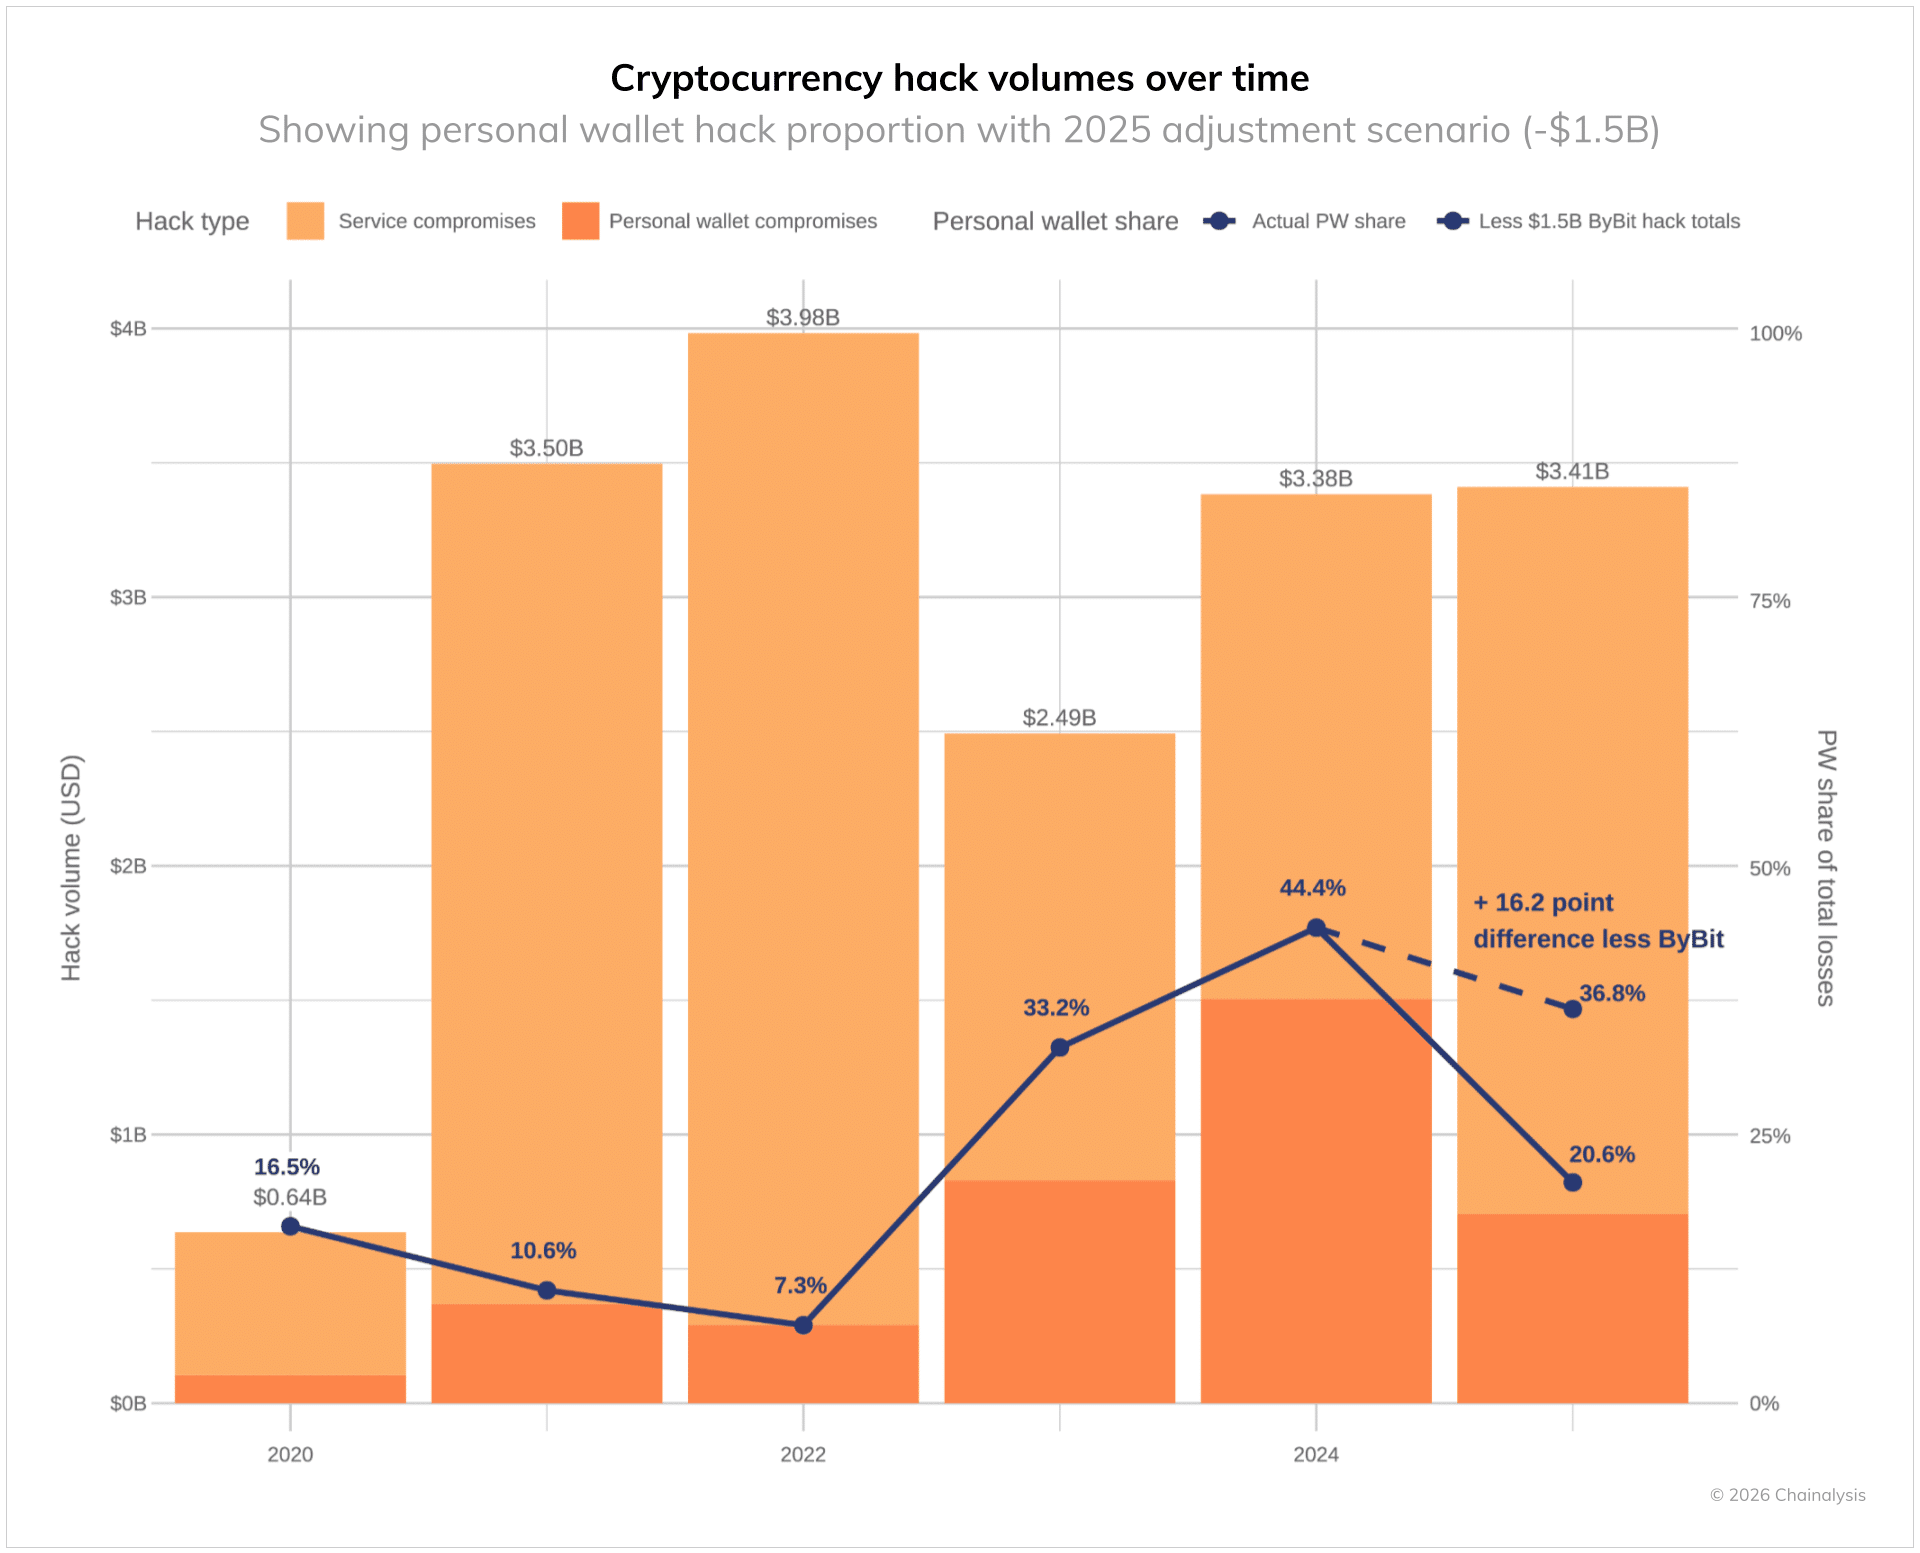
It also found that personal wallet compromises became a larger part of the loss picture, rising from 7.3% of stolen value in 2022 to 44% in 2024. 158,000 individual wallet-compromise incidents affected 80,000 unique victims in 2025, even as DeFi hack losses stayed suppressed despite higher TVL.
Read together, the data does not let either side win an easy argument.
On-chain code still fails. Off-chain systems clearly fail too. The more useful pattern is that large losses increasingly expose the machinery around the code: validators, signers, interfaces, wallet infrastructure, cloud systems, personal devices and human access. But the bigger danger begins after the first failure.
Why does one small mistake crash the whole system?
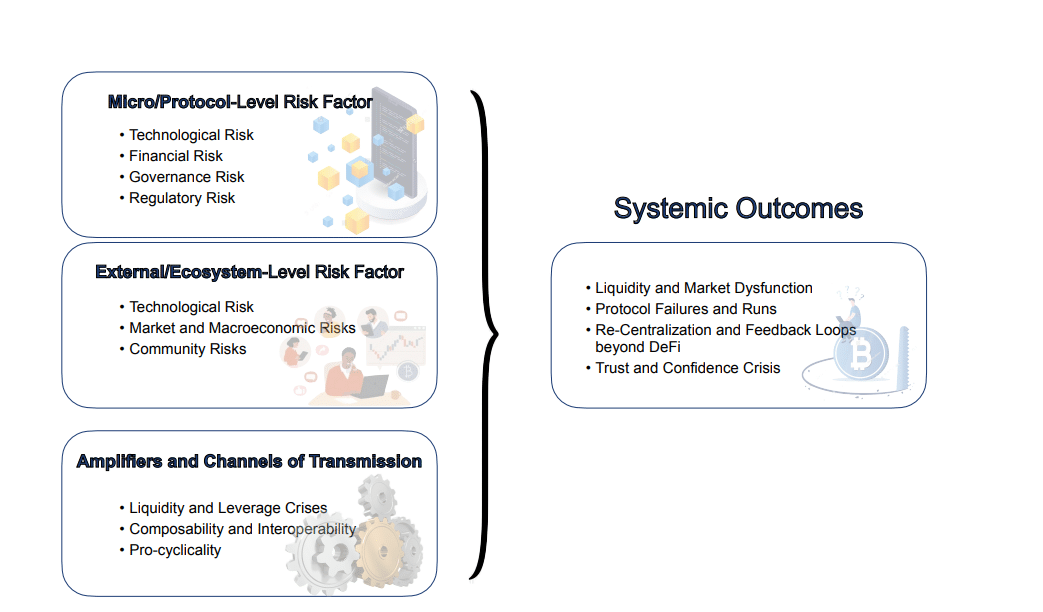
In DeFi, a broken assumption rarely stays where it starts. A bridge asset can become collateral. Collateral can support loans. Loans can feed vaults. Vaults can sit inside aggregators. By the time users see the headline, the risk may have already passed through several layers. That is where misdiagnosis becomes more than sloppy language.
For your context, in TradFi, if a bank fails, regulators might freeze assets while they figure out what happened. In DeFi, code executes automatically.
Once systems are connected, naming the wrong failure can distort how the market understands every exposure built on top of it.
Domino effect of interconnected risk
Composability is usually treated as DeFi’s great advantage. Protocols seamlessly plug into one another, assets migrate across chains, tokens double as collateral, and liquidity is recycled endlessly across markets.
However, this frictionless design is a double-edged sword because the very architecture that accelerates growth also accelerates failure.
When a cross-chain bridge issues an asset, that asset rarely stays put. It travels. It enters lending markets, sits inside yield vaults, gets routed through aggregators, or serves as collateral for entirely separate positions.
If the bridge’s security model breaks, the damage cannot be contained to the bridge contract itself. Every downstream protocol that treated that bridged asset as a safe, pristine store of value suddenly inherits the rot.
This is where the “Money Lego” metaphor starts to look too clean.
XChainWatcher makes the bridge version of this problem clearer. The study found that bridge vulnerabilities have caused $3.2 billion in losses since May 2021, while also flagging failures that normal “DeFi hack” coverage can miss.
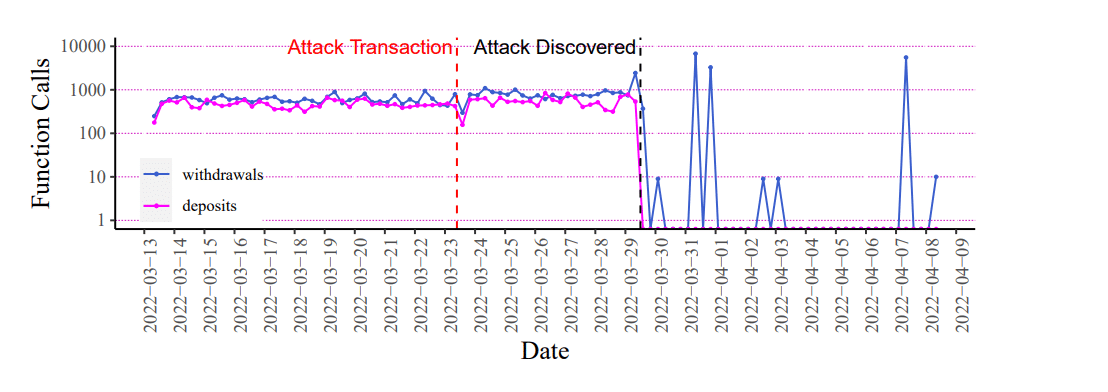
So, the first failure may begin as a bridge assumption, a signer, an oracle, or a governance path. The second-order failure is “trust” moving downstream. Toxins move through the financial plumbing long before the market even realizes a breach has occurred.
Better question is which layer failed
Did the code behave incorrectly? Was the protocol fed bad data? Did a bridge validator or multisig signer lose authority? Was a frontend or CI/CD pipeline compromised before users even saw the transaction? Did governance change the rules? Or was the person with access targeted directly?
Those questions lead to different answers.
Better audits matter, yes. They can reduce code-level risk. But they cannot solve stolen keys, compromised signers, weak bridge controls, exposed cloud credentials, and poor operational security. And, they definitely can’t stop people being targeted because they control access to crypto wealth.
That is the point of being precise. If the industry keeps mislabeling the failure, it will keep fighting the wrong battle.
“DeFi hack” may remain useful as a headline shortcut. As a diagnosis though, it is often too blunt to be true. Maybe the better question is where the failure actually began.
Final Summary
- DeFi protocols plug into one another seamlessly; a security breach at one foundational layer causes immediate downstream damage.
- An overwhelming majority of stolen funds are actually lost to off-chain operational failures, compromised signing keys, and human vulnerabilities.